Server-side credentials
Keep provider keys and secrets out of browser code, mobile bundles, public repositories and client-side logs.
PixelNestTech is designed around server-side secrets, signed requests, explicit access boundaries, webhook verification and auditable operational events.
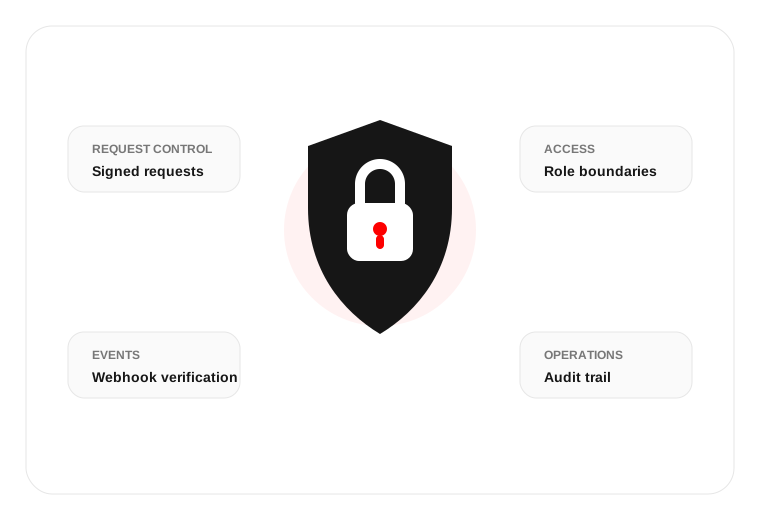
The platform design keeps provider credentials and privileged payment operations on trusted server-side infrastructure.
Keep provider keys and secrets out of browser code, mobile bundles, public repositories and client-side logs.
Use request signing or equivalent authentication controls where provider integrations require message integrity.
Validate event authenticity before applying payment state changes to your own systems.
Separate configuration, support and operational access according to the responsibilities of each team.
Retain references and event history needed to reconstruct what happened during a transaction lifecycle.
Treat retries and duplicate event delivery as expected behavior instead of exceptional behavior.